What is Continual Improvement in ISO 9001?
ISO certification work can stall when a Quality Management System is treated as a one-time documentation project. A compliant QMS has to become a working system that finds problems, responds to evidence, and improves the way the organization operates.
A practical way to build that capability is to implement the QMS in stages. After establishing the foundation processes, the second stage is continual improvement: putting corrective action, risk-based thinking, internal audits, customer feedback, and process measurement into regular use.
What Is Continual Improvement in ISO 9001?
Continual improvement in ISO 9001 is the recurring work of improving the suitability, adequacy, and effectiveness of the Quality Management System. It is not a single project or a requirement to change everything at once. It is a disciplined cycle of using objectives, audit findings, performance data, customer feedback, nonconformities, corrective actions, and identified risks and opportunities to decide what should improve next.
ISO guidance on improvement connects continual improvement to the wider management system. Clause 6 addresses planning, including risks, opportunities, and quality objectives. Clause 9 addresses performance evaluation. Clause 10 addresses improvement, nonconformity, corrective action, and continual improvement. Corrective Action is therefore a major mechanism, but it is not the whole improvement system.
How Should You Build the Continual Improvement Process?
The ISO QMS implementation project can be divided into four distinct phases. The phases provide a practical sequence rather than four isolated projects. Work started in one phase continues as later parts of the system are added.
| Phase One | Foundation Processes (primarily ISO 9001 Clause 4) |
| Phase Two | Continual Improvement Processes (supported by Clauses 6, 9, and 10) |
| Phase Three | Management Resources (primarily Clauses 5 and 7) |
| Phase Four | Data Management (operational control and performance evidence across Clauses 8 and 9) |
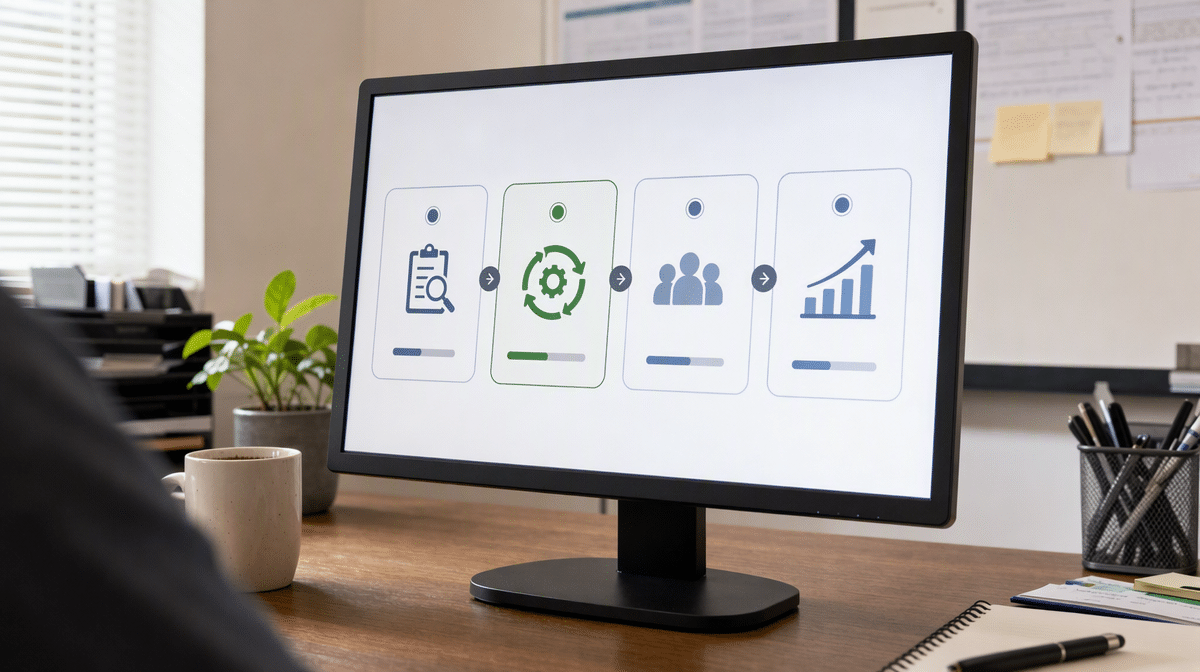
In phase one, after creating the project plan, the organization lays the foundation for its ISO implementation. That work includes becoming familiar with ISO 9001 QMS Requirements, identifying key QMS processes and their interaction, drafting the Quality Manual, Quality Policy, and Policy Objectives, and establishing controls for documented information and records.
After those foundation tasks are underway, phase two puts the continual improvement processes into practice. Starting early helps the organization learn from real work while the ISO QMS is still being built. It also produces useful evidence for management review, internal audits, and later certification readiness.
Sketch Out the Continual Improvement ISO Process
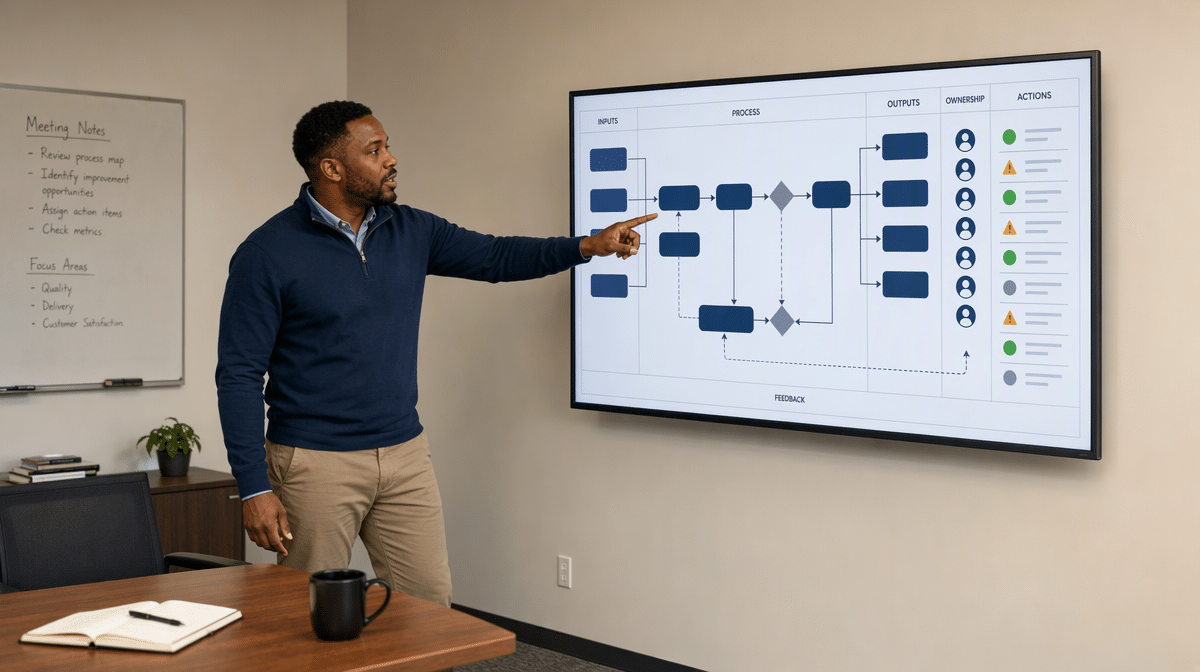
Much as you would for the critical QMS processes in phase one, sketch out the continual improvement processes. Ask practical questions: How will Corrective Actions benefit the organization? Who are the process owners? What are the inputs and outputs? Which departments are integral to continual improvement, and where should everyone get into the act?
Involve the ISO Strategy Team when resolving those questions. A cross-functional team can provide perspectives from different departments or segments of the organization, identify handoff risks, and make sure the process works beyond the quality department.
Draft the ISO 9001 Procedures You Need
Once you have sketched the process, create a procedure when documented instructions will help people perform it consistently. Document the process in the way the organization is capable of doing it, not how it should work in a perfect world. After you have a draft procedure, train the involved staff and start executing the process.
You don’t have to wait until the procedure is finalized or the ISO QMS is fully implemented to start executing Corrective Actions. A controlled draft creates an opportunity to learn which practices are effective, remove steps that do not work, and update documentation before weak habits become entrenched.
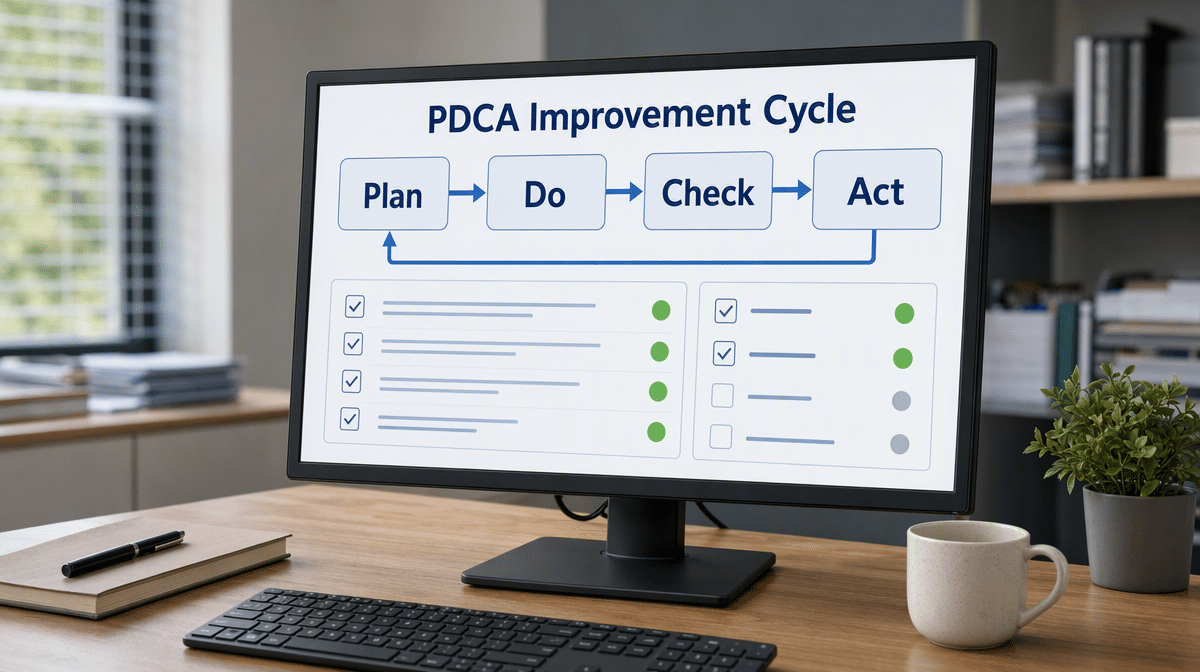
A common implementation mistake is over-documenting: writing too many procedures that are not followed, used, updated, or correct. ISO 9001 does not prescribe a fixed set of mandatory procedures. It requires documented information to the extent needed to support process operation and provide confidence that processes are carried out as planned. A practical Plan-Do-Check-Act cycle helps teams test a process, learn from evidence, and revise it without building unnecessary bureaucracy.
Which Processes Drive Continual Improvement?
Corrective Action, control of nonconforming outputs, Internal Audits, risk-based thinking, customer feedback, quality objectives, and analysis of data all support continual improvement. They do not need to exist as disconnected procedures. Their value comes from forming a working loop in which evidence leads to decisions, actions, and effectiveness checks.
Corrective Action
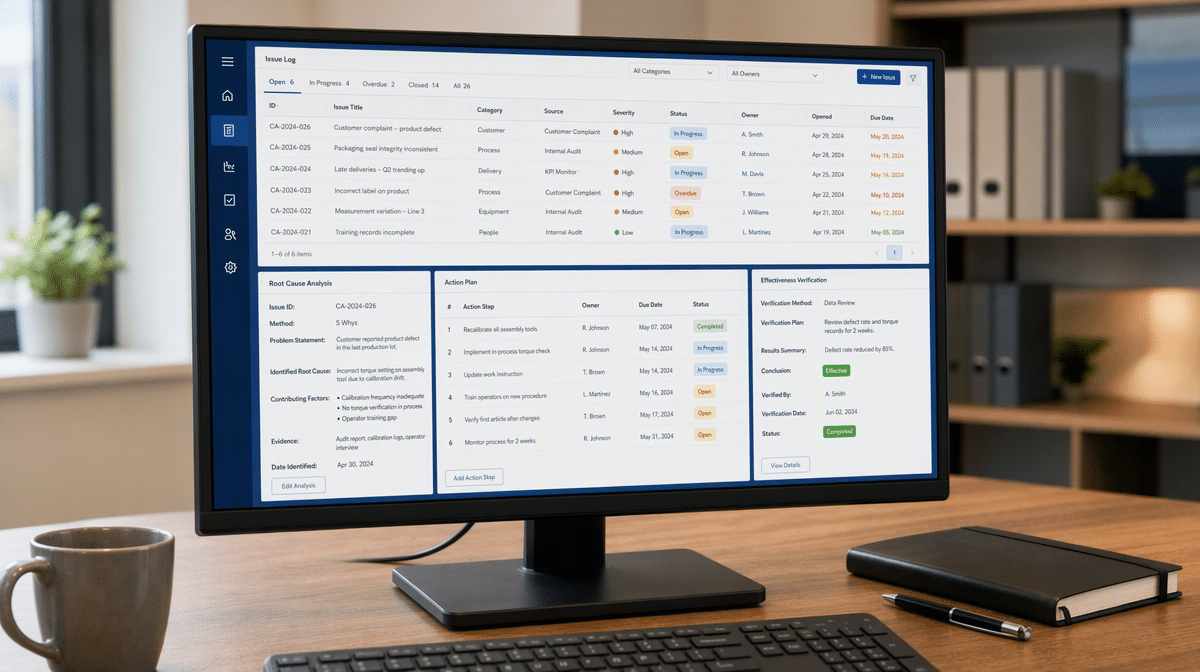
Corrective Action is the process used to eliminate the causes of a nonconformity so it does not recur. Problems may arise in office or production processes, products, services, suppliers, customer interactions, or the QMS itself. A sound corrective action process includes four basic steps:
- Control and correct the current problem, including its consequences.
- Investigate root causes and determine whether similar problems exist or could occur.
- Make the necessary corrections and improvements.
- Verify effectiveness by checking whether the problem recurs and whether the intended result is sustained.
The goal is not to close a form. The goal is to understand and change the system that allowed the problem to happen. Linking corrective action to root-cause problem solving keeps teams from repeatedly treating symptoms.
Risk-Based Thinking
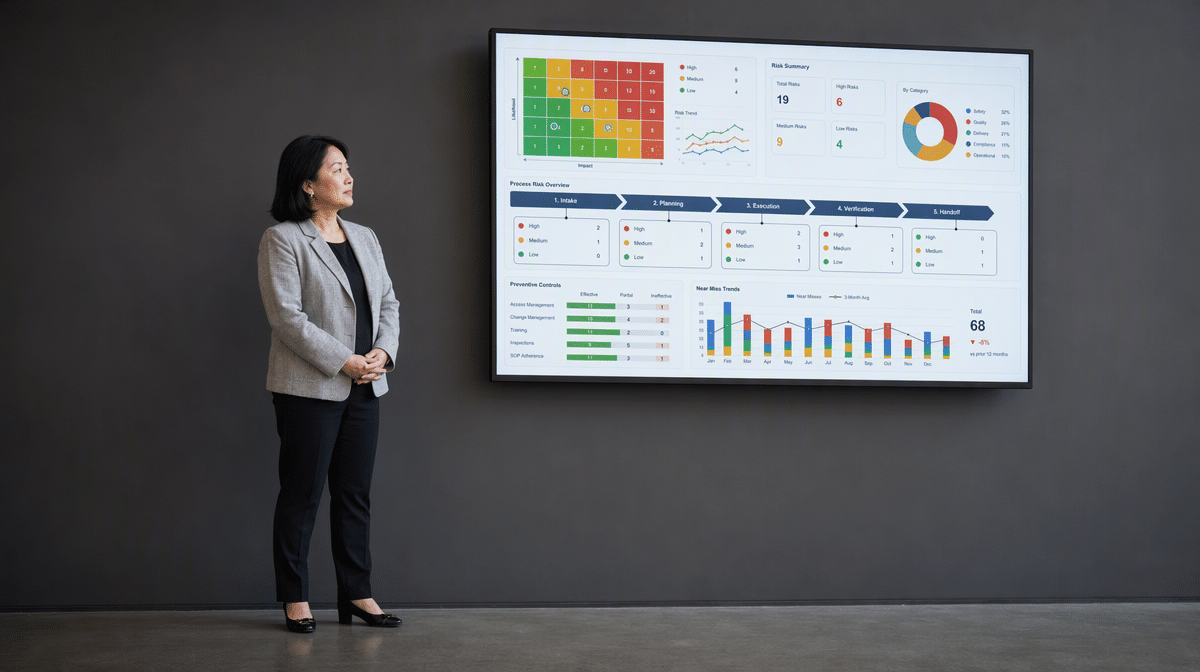
Risk-based thinking helps the organization act before problems occur and recognize opportunities to improve results. It is broader than the preventive action procedure used in older quality-system models. Risk is considered when setting objectives, designing processes, managing changes, selecting controls, and deciding how much evidence is needed.
Organizations sometimes struggle with prevention because they imagine every preventive measure must be big or expensive. Small improvements prevent problems as well. A clarified instruction, a better inspection point, a revised approval threshold, or a more useful near-miss review can reduce risk without creating bureaucracy.
Control of Nonconforming Outputs
Nonconforming outputs are products, services, information, or process results that do not meet a requirement. In manufacturing, that may include defects found during receiving inspection, production, or customer returns. In a service process, it may be an incomplete deliverable, a missed control, or an incorrect customer record.
Each nonconformity should be identified and controlled so it is not unintentionally used or delivered. The organization then determines an appropriate disposition. Patterns, severity, or recurrence may lead to a Corrective Action and a wider process improvement.
Internal Audits
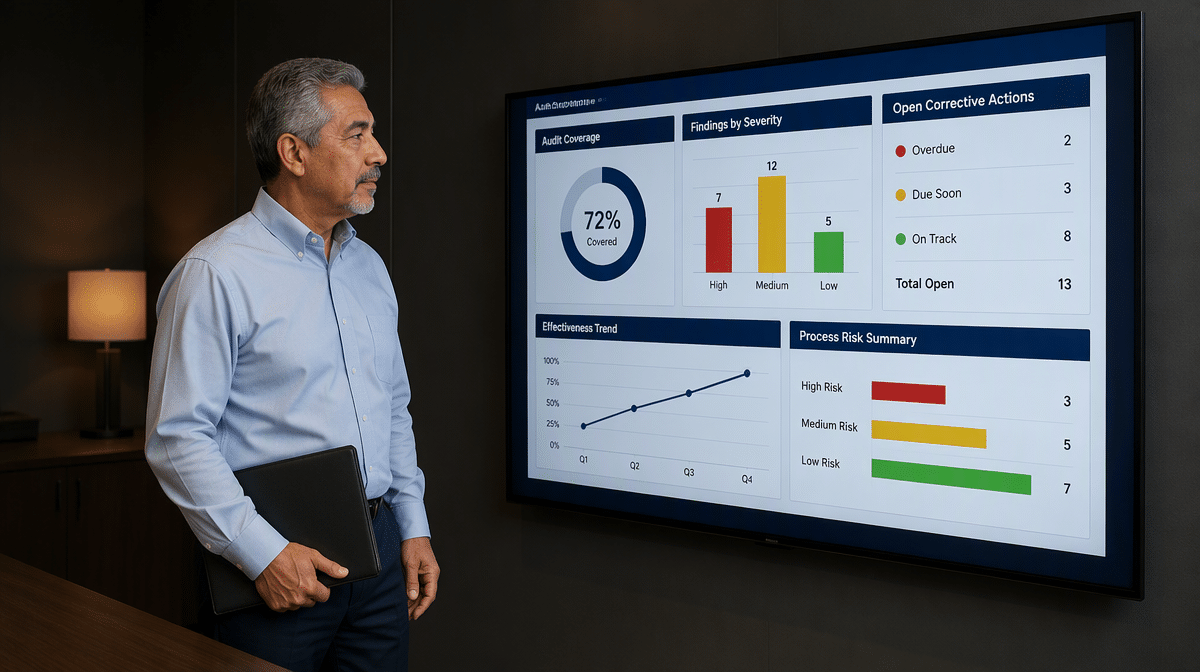
Internal Audits are instruments for measuring whether the ISO 9001 QMS conforms to planned arrangements and is effectively implemented and maintained. The internal audit team needs training, process knowledge, objectivity, and an understanding of ISO 9001 QMS Requirements. Audit findings then feed correction, corrective action, management review, and improvement priorities.
Internal auditing can begin before the entire system is implemented. Some records and documents may not yet be available, but auditors can examine the Foundation Processes already in place. Early audits provide ISO 9001 auditing practice, generate audit records, and show where the growing QMS needs attention.
Auditor Skills Require Risk-Based Approaches
Auditors should be able to recognize risk concepts, tools, and methods for risk analysis and management. ISO 31000 or Failure Mode and Effects Analysis are not required methods, but familiarity with a suitable risk-based approach helps auditors focus on issues that can materially affect process results.
Auditors also need to understand interested parties such as customers, employees, shareholders, board members, suppliers, competitors, and regulators. Their relevant requirements influence organizational context, process risks, and the evidence an audit should examine.
How Do You Address Risk and Measure Improvement?
Clause 6 is about planning for quality, including risks and opportunities that could affect intended results. ISO 31000:2018 provides principles and a framework for identifying, analyzing, evaluating, treating, monitoring, and communicating risk. ISO 9001 does not require ISO 31000, but the framework can help an organization make its risk process more systematic.
A common method is Failure Mode and Effects Analysis, or FMEA, which helps a team identify potential failure modes, consider their effects and causes, and prioritize action. A structured risk and opportunities process can help a team apply the method consistently enough to guide decisions and action.
Near misses are another useful signal. When defects are rare, measuring only failures can hide emerging weakness. Tracking close calls, control overrides, rework, recurring questions, or changes in process variation can reveal where prevention and continuous learning are needed before a customer is affected.
What Additional ISO System Components Support Continual Improvement?
Other pieces of continual improvement include customer satisfaction and analysis of data. The organization needs defined processes for capturing relevant customer perceptions and for regularly collecting and analyzing information from the critical processes identified in the Quality Manual.
Set measurable objectives for those processes, compare actual results with the objectives, and take action when performance falls short or an opportunity appears. Useful evidence may include complaints, returns, on-time delivery, audit results, rework, process capability, supplier performance, near misses, and progress against Quality Objectives. Management review brings that evidence together so leaders can decide priorities and provide resources.
Continual improvement provides value when the organization closes the loop: evidence leads to a decision, the decision leads to action, and the action is checked for effectiveness. With those processes operating, phase two of ISO implementation is no longer a set of documents. It is a repeatable way to strengthen the ISO 9001 QMS while the remaining system components are put in place.
Frequently Asked Questions
What Is Continual Improvement in ISO 9001?
Continual improvement is the recurring work of improving the suitability, adequacy, and effectiveness of the Quality Management System by using objectives, audits, data, feedback, nonconformities, risks, opportunities, and corrective actions.
Which ISO 9001 Clauses Support Continual Improvement?
Clause 6 supports planning and quality objectives, Clause 9 supports performance evaluation, and Clause 10 covers improvement, nonconformity, corrective action, and continual improvement. The complete QMS contributes evidence and resources to the cycle.
How Does Corrective Action Support Continual Improvement?
Corrective Action addresses the causes of a nonconformity so it does not recur. The process controls the current problem, investigates causes, implements changes, and verifies that those changes remain effective.
How Do Internal Audits Drive Continual Improvement?
Internal Audits compare actual practice with planned arrangements and evaluate whether the QMS is effectively implemented and maintained. Audit findings identify corrections, Corrective Actions, risks, and improvement priorities.
What Evidence Shows That Continual Improvement Is Working?
Evidence may include progress against Quality Objectives, fewer recurring nonconformities, effective Corrective Actions, improved customer satisfaction, stronger process results, useful audit findings, and reduced risk. Trends matter more than a single isolated result.