How to Use a Risk Assessment Matrix for Project Management

Every project has a quiet question sitting underneath the schedule, budget, and task list: what could go wrong? The teams that ask it early can usually protect the work before a small problem becomes a stalled launch, an overrun, or a customer-facing failure.
That question matters because business risk is not theoretical. The U.S. Bureau of Labor Statistics reported that 34.7 percent of business establishments born in 2013 were still operating in 2023. A practical risk assessment helps project teams identify likely obstacles, compare their impact, and decide where attention and resources should go first.
What Is a Risk Assessment Matrix?
A risk assessment matrix is a project management tool for ranking risks by likelihood and impact. In plain terms, it helps you compare what might happen, how likely it is to happen, and how much damage it could do if it does.
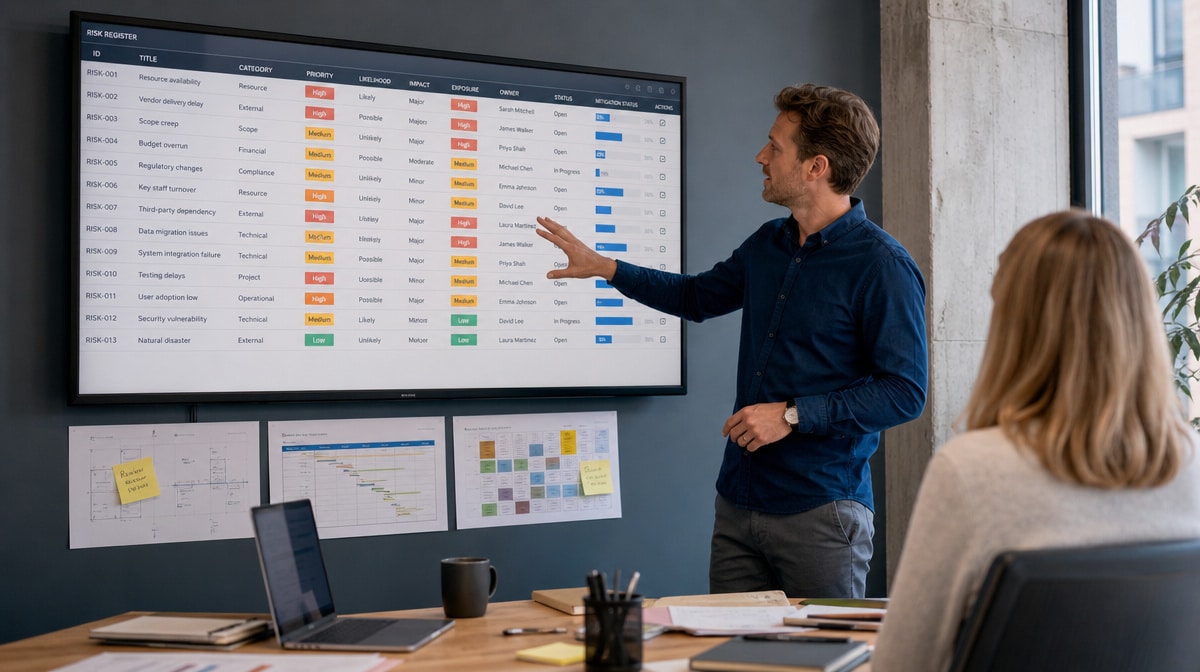
The matrix usually uses a grid. One axis measures probability, and the other measures impact. When you plot a project risk on the grid, it falls into a low, medium, high, or critical priority zone. That ranking turns a vague worry into a visible management decision.
For project managers, the matrix is useful because every project has more possible threats than available time. A vendor delay, a budget overrun, a compliance issue, a weak handoff, and a cybersecurity concern cannot all receive the same attention. The matrix gives the team a shared way to decide what deserves immediate action.
Start With Project Risk Identification
What threats await your project? The idea is to identify every obstacle that could stand in the way of success before the project is too far along to adjust. Start with past projects, missed deadlines, vendor issues, customer complaints, budget surprises, audit findings, and known resource constraints.
If the current project is different from past work, look for outside signals. Talk with people who have run similar projects, review industry requirements, study market conditions, and ask each functional owner where the plan is most fragile. A good risk list is not pessimistic. It is honest.
Keep the first pass broad. Include schedule risk, cost risk, quality risk, compliance risk, people risk, technology risk, vendor risk, and communication risk. You can narrow the list later. The early goal is visibility, not perfection.
Analyze the Threat
After the team identifies risks, each risk needs a short analysis. Some threats can maim an entire business project. Others are inconvenient but manageable. The matrix only works when the team agrees on what likelihood and impact mean.
Define likelihood in practical language. A low-likelihood risk might be possible but unusual. A high-likelihood risk might be expected unless the team acts. Define impact the same way. A low-impact risk might create minor rework, while a high-impact risk could stop the project, trigger a compliance problem, or require executive intervention.
The National Institute of Standards and Technology describes risk assessment as a process that considers threats, vulnerabilities, likelihood, impact, and the resulting level of risk in its Guide for Conducting Risk Assessments. Project teams do not need a federal risk program to use the idea. They need a consistent way to compare risk before making treatment decisions.
Why Using a Risk Assessment Matrix Matters
With limited resources and barely enough time to deal with all threats at the same time, it is essential to learn how to prioritize project risks. A risk assessment matrix can help you rank risks by multiplying or otherwise combining the probability of a threat occurring with the impact it could have on your business.
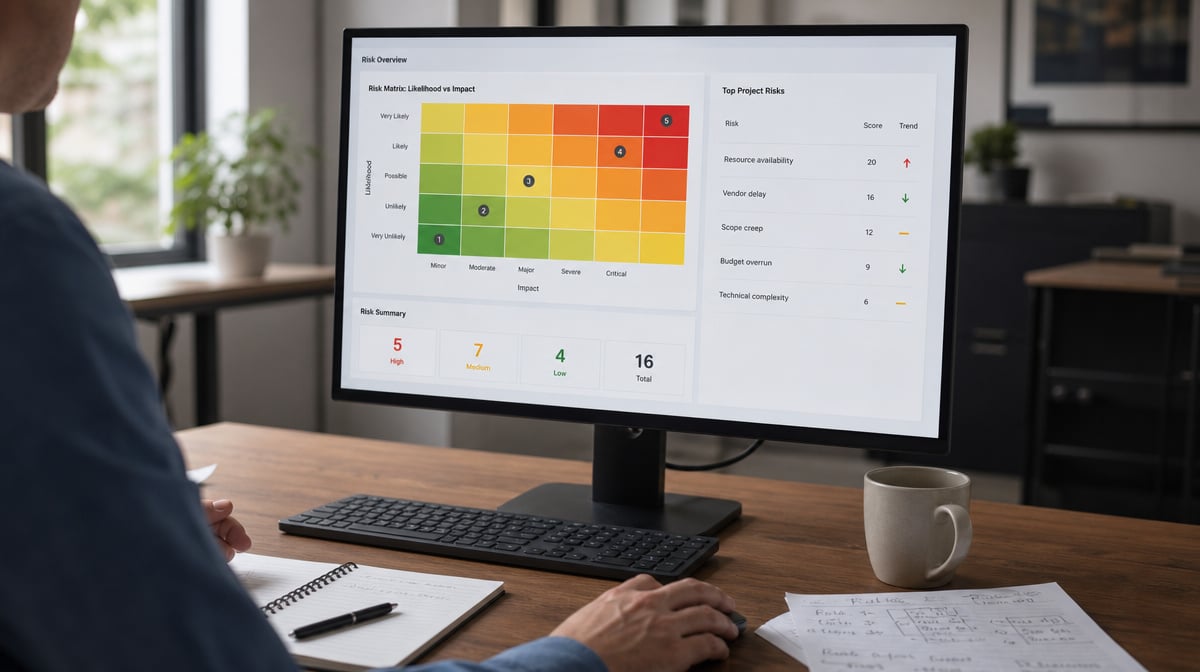
The score is not meant to replace judgment. It gives the team a starting point. A high-probability, high-impact risk should move toward the top of the register. A low-probability, low-impact risk can usually be monitored without consuming the project manager’s week.
The matrix also makes communication easier. When you forward risk treatment options to executive managers for approval, a color-coded matrix and short risk register are easier to understand than a long list of disconnected concerns. The executive team can see which threats need budget, which need owner attention, and which can be accepted.
Picking the Right Risk Treatment Method
The best risk treatment option depends on risk appetite, project constraints, and available resources. In project management, the common treatment choices are to avoid the risk, transfer the risk, reduce the risk, or accept the risk.
Avoid the Risk
Avoidance means changing the project plan so the risk no longer applies. If a feature depends on an unstable vendor integration, the team might remove that feature from the first release or choose a simpler approach.
Transfer the Risk
Transfer means moving responsibility to another party that is better prepared to manage the risk. A business might outsource a specialized cybersecurity task, require insurance, or use a contract clause that assigns responsibility to the vendor most able to control the exposure.
Reduce the Risk
Reduction means lowering the likelihood or impact. You might add testing, create a backup supplier, increase review frequency, assign a stronger project owner, or document a clearer approval process. Most project risks fall into this category.
Accept the Risk
Acceptance means the risk is real, but the cost of treatment is higher than the likely damage. This should be a conscious decision, not a failure to act. Record the decision, name the owner, and define what would cause the team to revisit it.
Employee Training Matters
For risk management to work, employees need to understand the role they play in reducing project risk. A risk treatment plan that sits in a spreadsheet will not protect the project if the people doing the work do not know what changed.
Training should match the risk. If the matrix shows that handoff errors are likely and costly, train teams on the handoff checklist. If vendor delay is the major exposure, train the project owner on escalation triggers. If cybersecurity could stop the project, train employees on the specific controls they are expected to follow.
The method matters as much as the content. Short scenario-based sessions, checklists, and manager-led reviews often work better than a long slide deck. The goal is not to make training feel clever. The goal is to make the risk control repeatable when the project is under pressure.
Monitor and Update the Risk Treatment Policies
With time, your project’s risk landscape will change. Resources shift, vendors miss commitments, budgets tighten, stakeholders add requirements, and new barriers appear. The sooner you make the necessary tweaks, the better.
Assign one person to own the risk register, but do not make risk monitoring a private activity. Review the matrix during project status meetings, update scores when conditions change, and make sure owners know which risks require action before the next meeting.
Comfort zones are a project’s recipe for failure. Once the team decides to take a risk, the review cadence should be clear. Be sure to integrate project management with a risk matrix so the project team can see which threats deserve attention first and which decisions need executive approval.
Download Free Policies and Procedures to see how easy it is to edit MS Word Templates to build your own policy and procedure management system.
Frequently Asked Questions
What Is a Risk Assessment Matrix in Project Management?
A risk assessment matrix is a grid that ranks project risks by likelihood and impact. It helps project teams decide which risks need immediate treatment, which should be monitored, and which can be accepted.
How Do You Score a Risk Matrix?
Most teams score a risk matrix by assigning a likelihood rating and an impact rating, then combining those ratings into a priority score. The exact scale can vary, but the team should define it before scoring risks.
Why Is Risk Identification Important Before Using the Matrix?
Risk identification gives the matrix useful inputs. If the team misses major project threats, the matrix will look organized but still fail to protect the project from the risks that matter most.
What Are the Main Risk Treatment Options?
The main risk treatment options are avoid, transfer, reduce, and accept. The right choice depends on the risk score, available resources, project constraints, and the organization’s risk appetite.
How Often Should a Project Risk Matrix Be Updated?
A project risk matrix should be updated whenever major project conditions change and reviewed during regular status meetings. High-priority risks should be checked more often than low-priority risks.