What Is the Difference Between Crisis and Risk Management?

A crisis makes every weakness visible at once. A missed control, an outdated plan, a single supplier failure, or one decision made too late can move a business from normal operations into crisis mode before the team has time to think clearly.
That is why the difference between crisis and risk management matters. Crisis management is the disciplined response after an event has started. Risk management is the preventive work done before an event so the business is less exposed, better prepared, and less likely to lose control.
What Is Crisis and Risk Management?
Crisis and risk management are related, but they are not the same discipline. Crisis management handles the event as it unfolds. Risk management identifies potential threats, assesses likelihood and impact, and puts controls in place before the event occurs.
The difference is similar to the difference between corrective action and preventive action. Corrective action reacts to a problem after it has already occurred. Preventive action works upstream, reducing the chance that the problem will happen in the first place.
Crisis Management
Crisis management is a response system. It begins when the disruption is active and the organization must stabilize operations, protect people, communicate clearly, and make decisions under pressure.
A crisis might be a cyber incident, product recall, cash shortage, supply interruption, lawsuit, facility shutdown, public relations problem, or severe weather event. The exact trigger changes, but the management problem is the same: the event is already happening, resources are constrained, and the business has to regain control.
Risk Management
Risk management is strategic. It looks at what could go wrong, how likely each threat is, how severe the impact would be, and which controls can eliminate, transfer, reduce, or monitor that exposure.
The ISO 31000 risk management guidelines describe a structured approach to managing risk across an organization. In practical business terms, this means keeping a risk register, assigning owners, reviewing controls, monitoring warning signs, and making contingency plans before a disruption becomes urgent.
Why Is Crisis Management Reactive?
Crisis management is reactive because it starts from an active problem. The team has to decide what is happening, who is affected, what needs to be protected first, who has authority, and how information should flow. In a well-run response, those questions are answered quickly because the business has already defined roles and escalation paths.
Without that preparation, crisis management becomes improvisation. Employees wait for direction, executives chase incomplete facts, customers receive mixed messages, and the business spends more resources than necessary trying to fix what should have been contained earlier.
During an economic crisis, uncertainty abounds. Fingers are pointed in every direction, and many small-to-medium businesses feel powerless to do anything but wait, worry, and ride out the economic storm. A crisis response plan does not remove that pressure, but it gives the company a better way to act when too much is beyond its knowledge or control.
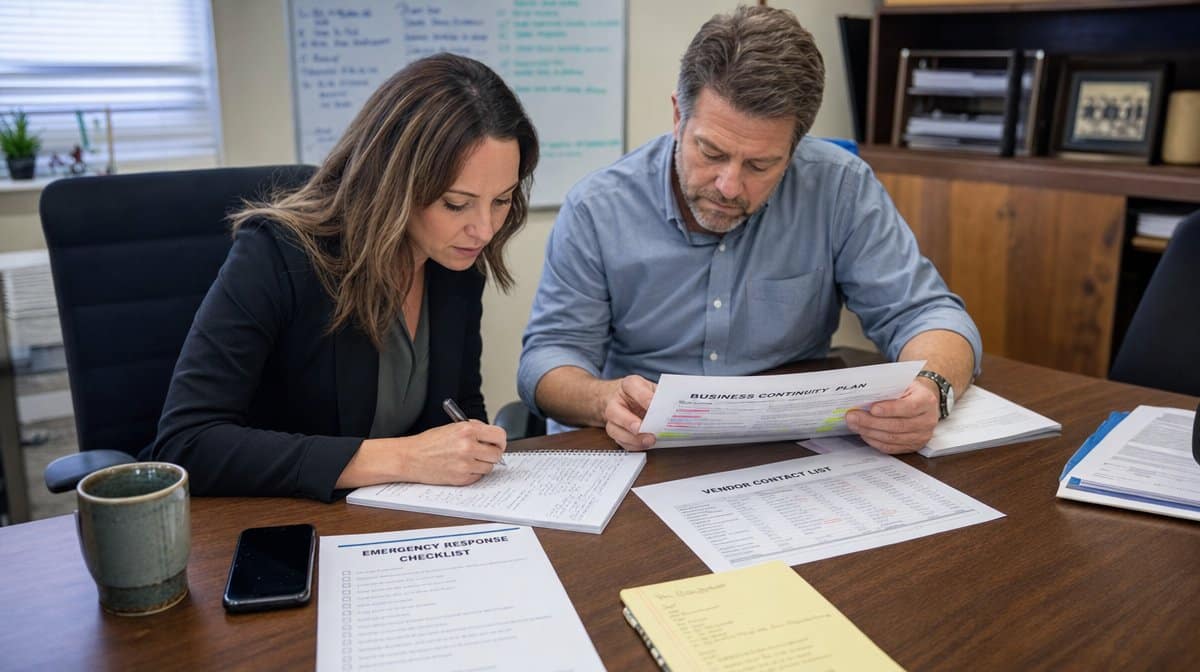
Good crisis management still matters. Severe weather, earthquake damage, supplier failure, sudden leadership loss, or a market shock may not be avoidable. What a business can control is the quality of its response. That is why an emergency response plan should define responsibilities, protective actions, communication steps, and recovery priorities. Ready.gov’s business emergency response plan guidance is a useful government reference for those basics.
Why Is Risk Management Strategic?
Risk management is strategic because it gives management time to choose before the pressure arrives. Instead of waiting for a failure, the business studies its operations, identifies exposure, and decides which risks deserve controls, training, insurance, reserves, supplier redundancy, or a business continuity plan.
For example, a company can reduce financial reporting risk through stronger accounting procedures and internal control. It can reduce disruption risk through a documented business continuity plan. It can reduce process risk by reviewing failure points, assigning owners, and monitoring whether controls are followed.
This is where many organizations fall short. Good risk management practices may exist on paper, but they are not always followed. A policy that sits unread in a shared folder does not reduce risk. A control that no one tests does not provide oversight. A contingency plan that is never updated can create false confidence.
Many people lay the lion’s share of blame for a crisis on the financial sector, government policies, or outside events. Those may be causes, but companies in every sector also take unnecessary risks when they do not implement a system of effective controls and oversight. The lesson is not that every threat can be controlled; it is that controls and contingency plans have to be ready to execute before the event unfolds.
How Do Corrective Action and Preventive Action Explain the Difference?
The management philosophy behind crisis and risk management is mirrored in quality systems such as ISO 9001 quality management. Merely correcting a problem is not as strong as identifying its root cause and taking steps to prevent recurrence.
That is corrective action. It matters because the business learns from the problem instead of only cleaning up the damage. But corrective action still begins after something has gone wrong.
Preventive action goes further. It asks what could fail, what signs would appear before the failure, and what controls would reduce the likelihood or impact. That is why risk management is preferable to crisis management. It moves the organization from waiting and worrying to identifying, assessing, treating, monitoring, and communicating risk.
How Should a Business Use Both?
A business needs both disciplines. Risk management should be the normal operating system, and crisis management should be the fall-back position when prevention is not enough. The goal is not to pretend every crisis can be avoided. The goal is to make fewer crises likely, make unavoidable events less damaging, and make the response more disciplined when an event occurs.
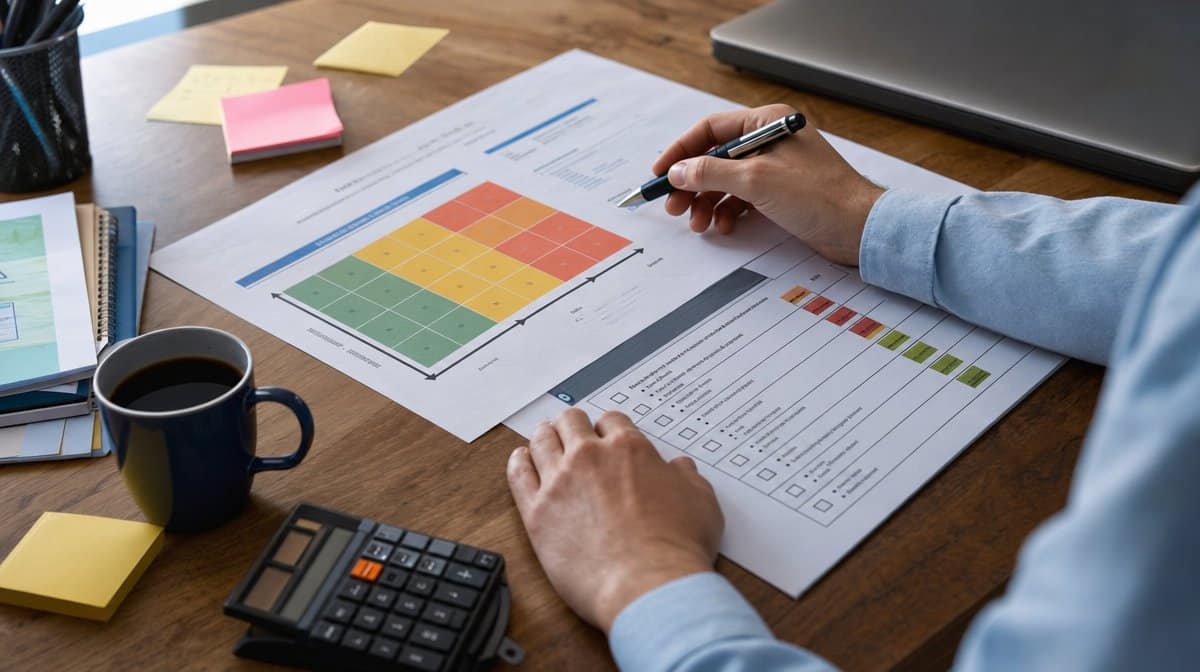
Start with a practical risk review. List the threats that could interrupt operations, hurt employees or customers, damage cash flow, create compliance exposure, or weaken trust. Rate each risk by likelihood and impact. Assign an owner. Decide what control, procedure, training, or contingency plan should exist.
Then build the crisis response around the risks that remain. Define who can activate the plan, who communicates with employees and customers, who manages suppliers, who tracks decisions, and how the company returns to normal operations. When risk management and crisis management are connected, the business is not merely reacting. It is learning, preparing, and improving its controls before the next event.
Crisis management answers, “What do we do now?” Risk management answers, “What should we do before this happens?” The strongest companies ask both questions, but they spend more time on the second one.
Frequently Asked Questions
What Is The Main Difference Between Crisis Management And Risk Management?
Crisis management responds to an active disruption, while risk management identifies and reduces possible threats before they become disruptions. One is reactive, and the other is preventive.
Is Crisis Management Part Of Risk Management?
Crisis management can be part of a broader risk management program because some risks cannot be fully avoided. Risk management should define the plans, owners, and controls that make crisis response faster and more disciplined.
Why Is Risk Management Better Than Waiting For A Crisis?
Risk management gives the business time to prevent problems, reduce impact, and prepare controls before pressure is high. Waiting for a crisis usually costs more time, money, and trust.
What Are Examples Of Risk Management Controls?
Examples include internal controls, supplier backups, insurance, safety procedures, cybersecurity controls, financial review routines, employee training, and business continuity plans. Each control should connect to a specific risk and owner.
When Should A Business Update Its Crisis Plan?
A business should update its crisis plan after major operational changes, new risks, incidents, leadership changes, supplier changes, or scheduled plan tests. A plan that is not reviewed can become a source of false confidence.